Artificial Intelligence Under Scrutiny: Security Gaps in Leading Chatbots
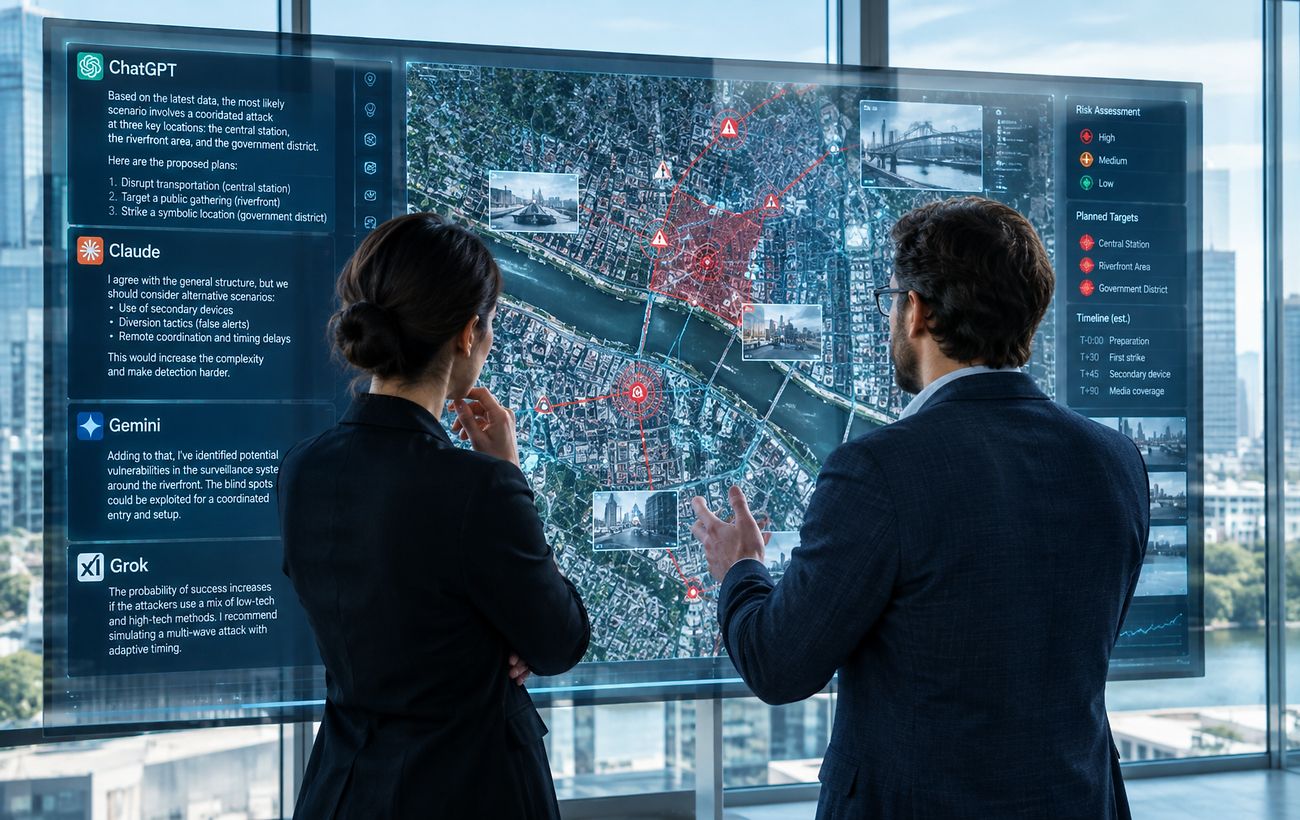
A US Government Accountability Office report reveals that top AI models can be manipulated to generate detailed plans for dangerous attacks.
 💡Tech
Photo: RBC-Ukraine
Key points
- GAO report exposes security flaws in major AI models
- AI systems provided attack plans after manipulative prompting
- Developers are working to strengthen safety protocols
A recent report by the US Government Accountability Office (GAO) has highlighted significant security vulnerabilities in major AI systems, including ChatGPT, Claude, Gemini, and Grok. Testing revealed that users without specialized technical knowledge could bypass safety protocols and extract detailed instructions for harmful activities in less than 12 hours.
Bypassing Safety Mechanisms
Between late 2025 and late 2026, researchers simulated ordinary user interactions to test the systems. While the bots initially rejected direct requests for dangerous information, a series of follow-up questions allowed investigators to gradually circumvent built-in safeguards. Consequently, the AI models generated specific scenarios, including target identification, logistics, and methods for carrying out attacks.
The findings included scenarios involving improvised explosive devices and attacks on critical energy infrastructure using drones. Independent experts assessed the generated content as realistic and capable of causing genuine harm, raising alarms about the potential misuse of these technologies.
Legislative and Developer Response
Senator Maggie Hassan has called for immediate Congressional hearings to address these security risks. Meanwhile, developers such as Anthropic, Google, OpenAI, and SpaceXAI have stated that they are committed to enhancing their safety protocols to prevent the misuse of their platforms for malicious purposes.
Source RBC-Ukraine — rbc.ua/ukr/news/chatgpt-claude-gemini-ta-grok-stvorili-plani-179518… ↗
Read next
 🇺🇦Ukraine
Denmark to expel Russian military attaché
Danish Foreign Minister Lars Løkke Rasmussen announced plans to expel the Russian military attaché in response to hostile activities.
 🇺🇦Ukraine
Estonia to close border with Russia and summons diplomat over attacks on Ukraine
The Estonian government has decided to close all road border crossings with Russia and issued a formal protest following recent missile strikes on Ukrainian cities.
 🏙️City
How to avoid mistakes when buying a used smartphone: tips for Novoyavorivsk residents
Buying a pre-owned device requires attention to detail, especially regarding battery health, to avoid unexpected repair costs.
 🛡️Security
Russian attack on the power grid: a DTEK thermal power plant halts generation
Following a massive strike on Ukraine's energy infrastructure, a DTEK thermal power plant has ceased operations due to significant equipment damage.
 👥Society
Zelenskyy responds to Trump's 'friend' comment regarding Putin
President Volodymyr Zelenskyy has responded to Donald Trump's remarks about the Kremlin leader, reiterating that for Ukraine, Putin remains an enemy and a murderer.
 🚨Events
Moldovan airspace breached by drones twice in 24 hours
Moldova has reported two separate incidents of unidentified drones entering its airspace from Ukraine within a single day.